

[Mar-2026] FCP_FCT_AD-7.4 Dumps are Available for Instant Access using ExamTorrent
FCP_FCT_AD-7.4 Dumps 2026 - New Fortinet FCP_FCT_AD-7.4 Exam Questions
NEW QUESTION # 35
A new chrome book is connected in a school's network.
Which component can the EMS administrator use to manage the FortiClient web filter extension installed on the Google Chromebook endpoint?
- A. FortiClient customer URL list
- B. FortiClient web filter extension
- C. FortiClient site categories
- D. FortiClient EMS
Answer: B
Explanation:
For managing the FortiClient web filter extension installed on the Google Chromebook endpoint, the EMS administrator can use the following component:
* FortiClient EMS (Enterprise Management Server)is designed to manage and control multiple FortiClient installations across various endpoints.
* EMS provides centralized management for endpoint policies, including web filtering configurations.
* The EMS administrator can configure and enforce web filter policies on Chromebooks through the EMS console.
Therefore, FortiClient EMS is the correct component for managing the web filter extension on Google Chromebook endpoints.
References
* FortiClient EMS 7.2 Study Guide, Chromebook Management Section
* Fortinet Documentation on FortiClient EMS and Web Filtering for Chromebooks
NEW QUESTION # 36
Refer to the exhibit.
Why is the user not able to access bbc.com? (Choose one answer)
- A. The URL is blocked by the web filter endpoint profile.
- B. The endpoint cannot resolve the URL FQDN.
- C. The application firewall is blocking Google Chrome.
- D. FortiGuard servers are not reachable from the endpoint.
Answer: D
Explanation:
Based on theFortiClient EMS Administrator Study GuideregardingWeb Filtertroubleshooting and the specific log entries provided in the exhibit, the reason the user cannot access the website is due to connectivity issues with FortiGuard.
1. Analysis of the FortiClient Logs:
* The Error Message:The logs show multiple [ERROR] entries stating: rating_db:97 Category query failure: failed to UrlRequestSendReceive.
* Root Cause Identity:The log explicitly describes the failure: receiveResponse error: FortiGuard server down, task dropped, https bbc.com.
* Resulting Action:Because the endpoint could not receive a rating from the FortiGuard servers, the Web Filter module recorded rating: -1 and applied the action WF_ACTION_BLOCK.
2. Why Option C is Correct:
* FortiGuard Dependency:FortiClient's Web Filter module relies on real-time queries to FortiGuard distribution servers to categorize URLs. If the endpoint is behind a firewall blocking FortiGuard ports (typically UDP 53 or 8888, or HTTPS 443) or has no internet path to these servers, it cannot categorize the site.
* Fail-Safe Behavior:In many FortiClient configurations, if a rating cannot be obtained (Category query failure), the default security posture is to block the request to ensure no potentially malicious or unrated
"Unknown" sites are accessed. The logs confirm this by showing the "FortiGuard server down" message immediately followed by the block action.
3. Why Other Options are Incorrect:
* A. The URL is blocked by the web filter endpoint profile:If it were a standard profile block, the log would show a specificCategory ID(e.g., Category 52 for News and Media) being blocked by policy.
Instead, it shows arating failure (-1).
* B. The endpoint cannot resolve the URL FQDN:The logs show the process correctly identifies host bbc.com. If DNS had failed, the proxy wouldn't even reach the stage of attempting a FortiGuard category query for that specific URL.
* D. The application firewall is blocking Google Chrome:While the log mentions /opt/google/chrome
/chrome, the error is generated by the rating_db and proxy components of the Web Filter, not the Application Firewall module.
NEW QUESTION # 37
Why does FortiGate need the root CA certificate of FortiCient EMS?
- A. To trust certificates issued by FortiClient EMS
- B. To revoke FortiClient client certificates
- C. To sign FortiClient CSR requests
- D. To update FortiClient client certificates
Answer: B
Explanation:
* Understanding the Need for Root CA Certificate:
* The root CA certificate of FortiClient EMS is necessary for FortiGate to trust certificates issued by FortiClient EMS.
* Evaluating Use Cases:
* FortiGate needs the root CA certificate to establish trust and validate certificates issued by FortiClient EMS.
* Conclusion:
* The primary reason FortiGate needs the root CA certificate of FortiClient EMS is to trust certificates issued by FortiClient EMS.
References:
FortiClient EMS and FortiGate certificate management documentation from the study guides.
NEW QUESTION # 38
Which statement about FortiClient enterprise management server is true?
- A. It provides centralized management of Chromebooks running real-time protection
- B. It provides centralized management of FortiClient Android endpoints only.
- C. lt provides centralized management of multiple endpoints running FortiClient software.
- D. It provides centralized management of FortiGate devices.
Answer: C
Explanation:
FortiClient EMS is designed to provide centralized management and control of multiple endpoints running FortiClient software. It serves as a central management server that allows administrators to efficiently manage and configure a large number of FortiClient installations across the network.
NEW QUESTION # 39
Which two statements are true about the ZTNA rule? (Choose two.)
- A. It applies SNAT to protect traffic.
- B. It enforces access control.
- C. It applies security profiles to protect traffic
- D. It defines the access proxy.
Answer: B,C
Explanation:
* Understanding ZTNA Rule Configuration:
* The ZTNA rule configuration shown in the exhibit defines how traffic is managed and controlled based on specific tags and conditions.
* Evaluating Rule Components:
* The rule includes security profiles to protect traffic by applying various security checks (A).
* The rule also enforces access control by determining which endpoints can access the specified resources based on the ZTNA tag (D).
* Eliminating Incorrect Options:
* SNAT (Source Network Address Translation) is not mentioned as part of this ZTNA rule.
* The rule does not define the access proxy but uses it to enforce access control.
* Conclusion:
* The correct statements about the ZTNA rule are that it applies security profiles to protect traffic (A) and enforces access control (D).
References:
ZTNA rule configuration documentation from the study guides.
NEW QUESTION # 40
Which statement about the FortiClient enterprise management server is true?
- A. It provides centralized management of multiple endpoints running FortiClient software.
- B. It receives the CA certificate from FortiGate to validate client certrficates.
- C. It enforces compliance on the endpoints using tags
- D. It receives the configuration information of endpoints from ForuGate.
Answer: C
NEW QUESTION # 41
Refer to the exhibit.
Which behavior should you expect when FortiClient with an invalid certificate is connecting to FortiClient EMS? (Choose one answer)
- A. FortiClient requires an additional password to connect to FortiClient EMS.
- B. FortiClient EMS pushes a valid certificate to FortiClient.
- C. FortiClient displays a warning message to the end user.
- D. FortiClient is blocked from connecting to FortiClient EMS.
Answer: C
Explanation:
Based on theFortiClient EMS 7.2/7.4 Administration Guideand the provided exhibit of theSystem Settings Profile, the expected behavior for an invalid certificate connection is determined by theInvalid Certificate Actionsetting.
1. Analysis of the Exhibit
* Location:The exhibit shows theSystem Settings Profile(specifically the "Default" profile).
* Setting:At the bottom under theEndpoint Controlsection, the fieldInvalid Certificate Actionis configured.
* Selected Action:The dropdown forInvalid Certificate Actiondisplays awarning icon(an orange triangle with an exclamation mark). In the FortiClient EMS GUI, this specific icon corresponds to the
"Warn"action.
2. Verified Behavior (Option C)
According to the curriculum documents regardingEndpoint Communication Security:
* Warn Action Behavior:When theInvalid Certificate Actionis set toWarn, FortiClient is instructed to display a warning message to the end user if the EMS server certificate is untrusted, expired, or has a hostname mismatch.
* User Prompt:The warning message explicitly asks the user whether they wish to proceed with the connection despite the security risk or terminate the attempt.
* Connection Logic:If the user manually accepts the warning, FortiClient will establish the Telemetry connection and "remember" the certificate for future sessions to avoid repeated prompts for that specific server.
3. Why Other Options are Incorrect
* A. FortiClient is blocked:This behavior only occurs if the administrator selects the"Deny"action in the profile.
* B. Additional password required:The password field shown at the top of the exhibit is for"Require Password to Disconnect From EMS", which prevents users from manually unregistering, but it does not bypass or resolve certificate errors.
* D. EMS pushes a valid certificate:EMS cannot "push" a valid identity certificate to resolve a failed TLS handshake; a valid certificate must be manually installed on the EMS server by the administrator.
NEW QUESTION # 42
Which two VPNtypes can a FortiClientendpoint user inmate from the Windows command prompt? (Choose two)
- A. L2TP
- B. PPTP
- C. SSL VPN
- D. IPSec
Answer: C,D
NEW QUESTION # 43
Refer to the exhibits.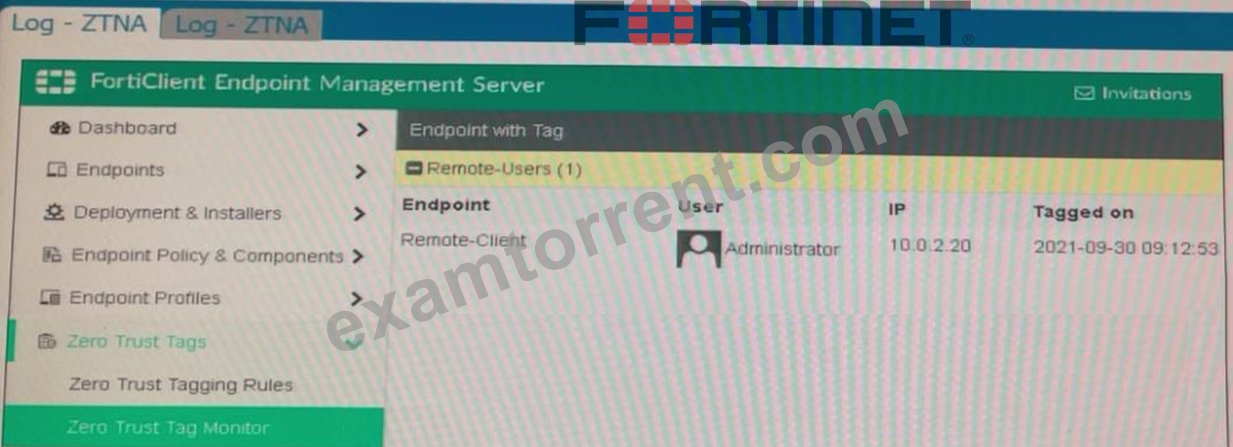
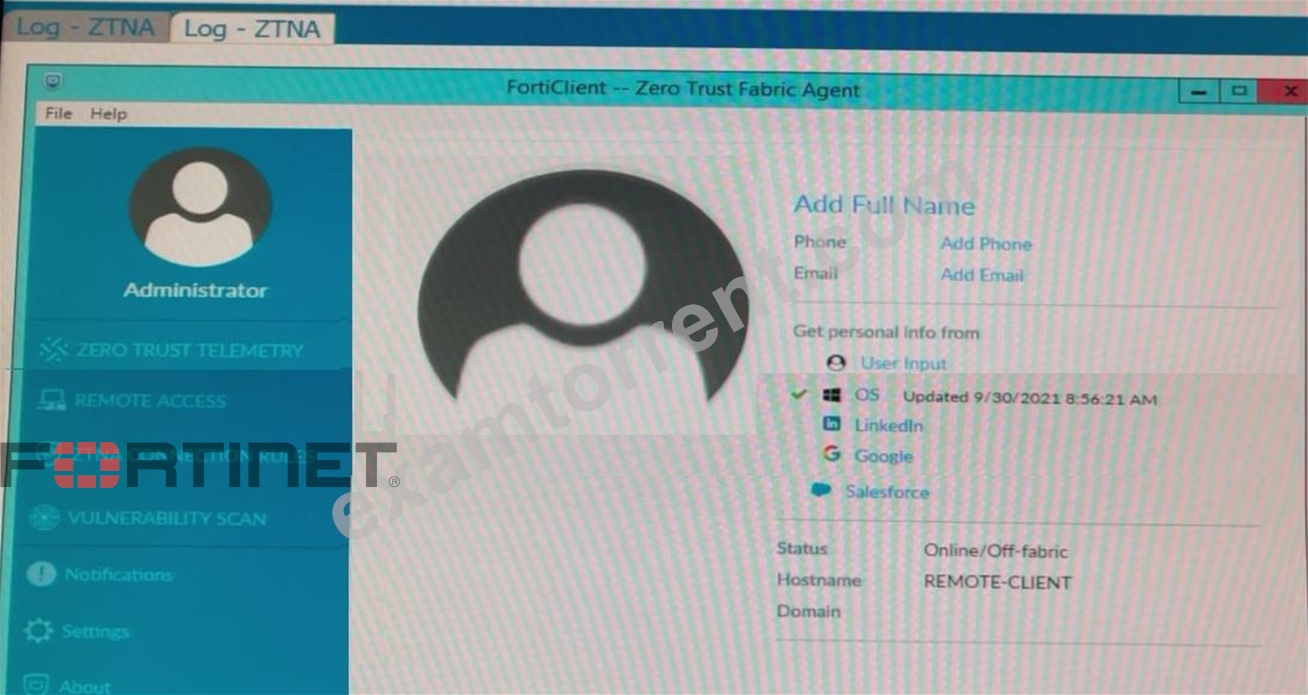
Which show the Zero Trust Tag Monitor and the FortiClient GUI status.
Remote-Client is tagged as Remote-Users on the FortiClient EMS Zero Trust Tag Monitor.
What must an administrator do to show the tag on the FortiClient GUI?
- A. Change the endpoint control setting to enable tag visibility
- B. Update tagging rule logic to enable tag visibility
- C. Change the user identity settings to enable tag visibility
- D. B. Change the FortiClient system settings to enable tag visibility
Answer: D
Explanation:
Based on the exhibits provided:
* The "Remote-Client" is tagged as "Remote-Users" in the FortiClient EMS Zero Trust Tag Monitor.
* To ensure that the tag "Remote-Users" is visible in the FortiClient GUI, the system settings within FortiClient need to be updated to enable tag visibility.
* The tag visibility feature is controlled by FortiClient system settings which manage how tags are displayed in the GUI.
Therefore, the administrator needs to change the FortiClient system settings to enable tag visibility.
References
* FortiClient EMS 7.2 Study Guide, Zero Trust Tagging Section
* FortiClient Documentation on Tag Management and Visibility Settings
NEW QUESTION # 44
FortiClient EMS endpoint policies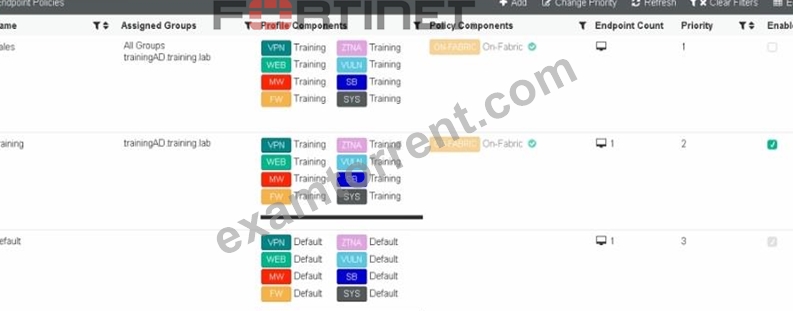
Refer to the exhibit, which shows multiple endpoint policies on FortiClient EMS. Which policy is applied to the endpoint in the AD group trainingAD
- A. The Default policy because it has the highest priority
- B. The sales policy
- C. The Training policy
- D. Both the Sales and Training policies because their priority is higher than the Default policy
Answer: C
Explanation:
* Observation of Endpoint Policies:
* The exhibit shows multiple endpoint policies with their assigned groups, priority levels, and enabled status.
* Evaluating Policy Assignment:
* The Training policy is specifically assigned to the "trainingAD.training.lab" group, with a higher priority than the Default policy.
* Conclusion:
* The correct policy applied to the endpoint in the AD group "trainingAD" is the Training policy (A).
References:
FortiClient EMS policy configuration and priority management documentation from the study guides.
NEW QUESTION # 45
Which three features does FortiClient endpoint security include? (Choose three.)
- A. L2TP
- B. DLP
- C. lPsec
- D. Real-lime protection
- E. Vulnerability management
Answer: C,D,E
Explanation:
* Understanding FortiClient Features:
* FortiClient endpoint security includes several features aimed at protecting and managing endpoints.
* Evaluating Feature Set:
* Vulnerability management is a key feature of FortiClient, helping to identify and address vulnerabilities (B).
* IPsec is supported for secure VPN connections (D).
* Real-time protection is crucial for detecting and preventing threats in real-time (E).
* Eliminating Incorrect Options:
* Data Loss Prevention (DLP) (A) is typically managed by FortiGate or FortiMail.
* L2TP (C) is a protocol used for VPNs but is not specifically a feature of FortiClient endpoint security.
References:
FortiClient endpoint security features documentation from the study guides.
NEW QUESTION # 46
Refer to the exhibit, which shows the Zero Trust Tagging Rule Set configuration.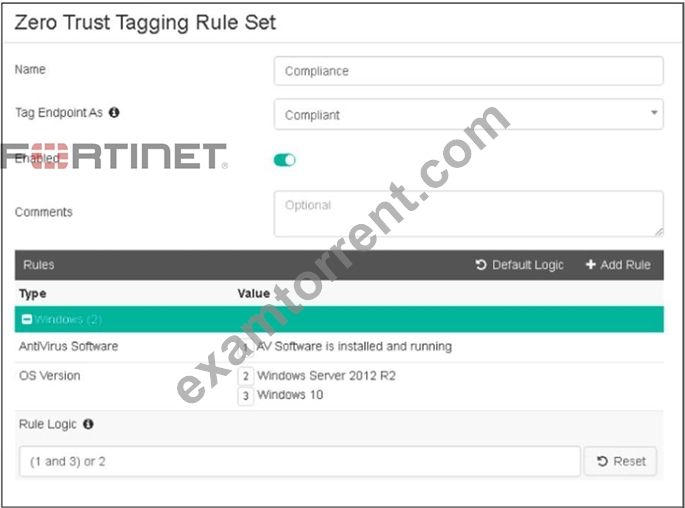
Which two statements about the rule set are true? (Choose two.)
- A. The endpoint must satisfy that only Windows 10 is running.
- B. The endpoint must satisfy that only Windows Server 2012 R2 is running.
- C. The endpoint must satisfy that antivirus is installed and running and Windows 10 is running.
- D. The endpoint must satisfy that only AV software is installed and running.
Answer: B,C
Explanation:
Based on the Zero Trust Tagging Rule Set configuration shown in the exhibit:
* The rule set includes two conditions:
* AV Software is installed and running
* OS Version is Windows Server 2012 R2 or Windows 10
* The Rule Logic is specified as "(1 and 3) or 2," meaning:
* The endpoint must have antivirus software installed and running and must be running Windows
10.
* Alternatively, the endpoint must be running Windows Server 2012 R2.
Therefore, the endpoint must satisfy either:
* Antivirus is installed and running and Windows 10 is running.
* Windows Server 2012 R2 is running.
References
* FortiClient EMS 7.2 Study Guide, Zero Trust Tagging Rule Set Configuration Section
* Fortinet Documentation on Configuring Zero Trust Tagging Rules and Logic
NEW QUESTION # 47
Refer to the exhibit.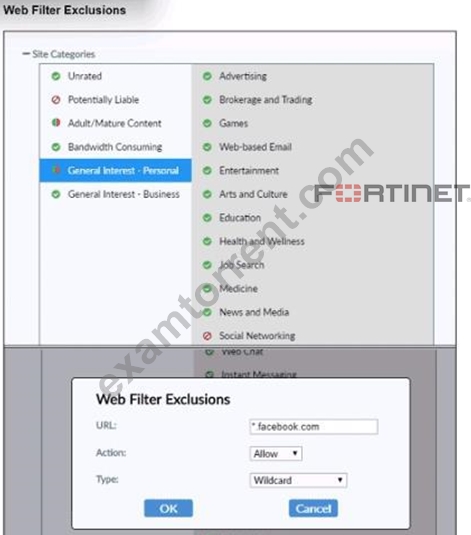
Based on the settings shown in the exhibit, which action will FortiClient take when users try to access www facebook com?
- A. FortiClient will allow access to Facebook.
- B. FortiClient will monitor only the user's web access to the Facebook website
- C. FortiClient will block access to Facebook and its subdomains.
- D. FortiClient will prompt a warning message to want the user before they can access the Facebook website
Answer: C
Explanation:
* Observation of Web Filter Exclusions:
* The exhibit shows a web filter exclusion for "*.facebook.com" with the action set to "Allow."
* Evaluating Actions:
* This configuration means that FortiClient will allow access to Facebook and its subdomains.
* Conclusion:
* When users try to access "www.facebook.com," FortiClient will allow the access based on the web filter exclusion settings.
References:
FortiClient web filter configuration and exclusion documentation from the study guides.
NEW QUESTION # 48
An administrator installs FortiClient on Windows Server.
What is the default behavior of real-time protection control?
- A. Real-time protection is disabled
- B. Real-time protection sends malicious files to FortiSandbox when the file is not detected locally
- C. Real-time protection must update the signature database from FortiSandbox
- D. Real-time protection must update AV signature database
Answer: A
Explanation:
When FortiClient is installed on a Windows Server, the default behavior for real-time protection control is:
* Real-time protection is disabled:By default, FortiClient does not enable real-time protection on server installations to avoid potential performance impacts and because servers typically have different security requirements compared to client endpoints.
Thus, real-time protection is disabled by default on Windows Server installations.
References
* FortiClient EMS 7.2 Study Guide, Real-time Protection Section
* Fortinet Documentation on FortiClient Default Settings for Server Installations
NEW QUESTION # 49
An administrator installs FortiClient EMS in the enterprise.
Which component is responsible for enforcing protection and checking security posture?
- A. FortiClient EMS tags
- B. FortiClient vulnerability scan
- C. FortiClient
- D. FortiClient EMS
Answer: C
Explanation:
* Understanding FortiClient EMS Components:
* FortiClient EMS manages and configures endpoint security settings, while FortiClient installed on the endpoint enforces protection and checks security posture.
* Evaluating Responsibilities:
* FortiClient performs the actual enforcement of security policies and checks the security posture of the endpoint.
* Conclusion:
* The component responsible for enforcing protection and checking security posture is FortiClient (C).
References:
FortiClient EMS and endpoint security documentation from the study guides.
NEW QUESTION # 50
An administrator deploys a FortiClient installation through the Microsoft AD group policy After installation is complete all the custom configuration is missing.
What could have caused this problem?
- A. FortiClient does not have permission to access the distribution package.
- B. The FortiClient MST file is missing from the distribution package
- C. The FortiClient package is not assigned to the group
- D. The FortiClient exe file is included in the distribution package
Answer: C
Explanation:
When deploying FortiClient via Microsoft AD Group Policy, it is essential to ensure that the deployment package is correctly assigned to the target group. The absence of custom configuration after installation can be due to several reasons, but the most likely cause is:
* Deployment Package Assignment:The FortiClient package must be assigned to the appropriate group in Group Policy Management. If this step is missed, the installation may proceed, but the custom configurations will not be applied.
Thus, the administrator must ensure that the FortiClient package is correctly assigned to the group to include all custom configurations.
References
* FortiClient EMS 7.2 Study Guide, Deployment and Installation Section
* Fortinet Documentation on FortiClient Deployment using Microsoft AD Group Policy
NEW QUESTION # 51
Exhibit.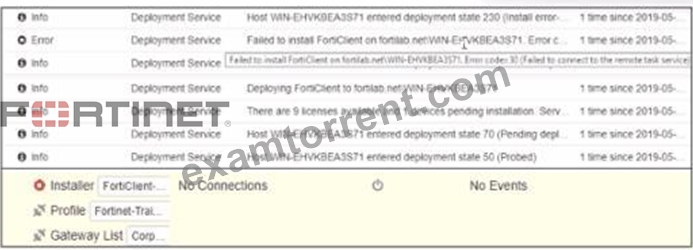
Based on the logs shown in the exhibit, why did FortiClient EMS tail to install FortiClient on the endpoint?
- A. The task scheduler service is not running.
- B. The Windows installer service is not running.
- C. The FortiClient antivirus service is not running.
- D. The remote registry service is not running.
Answer: A
Explanation:
https://community.fortinet.com/t5/FortiClient/Technical-Note-FortiClient-fails-to-install-from-FortiClient- EMS/ta-p/193680 The deployment service error message may be caused by any of the following. Try eliminating them all, one at a time.
1. Wrong username or password in the EMS profile
2. Endpoint is unreachable over the network
3. Task Scheduler service is not running
4. Remote Registry service is not running
5. Windows firewall is blocking connection
NEW QUESTION # 52
An administrator must add an authentication server on FortiClient EMS in a different security zone that cannot allow a direct connection.
Which solution can provide secure access between FortiClient EMS and the Active Directory server?
- A. Configure a slave FortiClient EMS on a virtual machine.
- B. Configure Active Directory and install FortiClient EMS on the same VM.
- C. Configure and deploy a FortiGate device between FortiClient EMS and the Active Directory server.
- D. Configure an Active Directory connector between FortiClient EMS and the Active Directory server.
Answer: C
Explanation:
* Requirement:
* The administrator needs to add an authentication server on FortiClient EMS in a different security zone that cannot allow a direct connection.
* Solution Analysis:
* The goal is to securely connect FortiClient EMS and the Active Directory server despite being in different security zones.
* Evaluating Options:
* Installing FortiClient EMS on the same VM as Active Directory (option B) is not practical due to security zone separation.
* Configuring a slave FortiClient EMS on a virtual machine (option C) does not address the need for secure communication.
* Configuring an Active Directory connector (option D) may not be sufficient without secure routing.
* Conclusion:
* Deploying a FortiGate device between FortiClient EMS and the Active Directory server ensures secure and controlled access between the two zones.
References:
FortiClient EMS and FortiGate configuration and deployment documentation from the study guides.
NEW QUESTION # 53
What does FortiClient do as a fabric agent? (Choose two.)
- A. Provides IOC verdicts
- B. Creates dynamic policies
- C. Automates Responses
- D. Provides application inventory
Answer: C,D
NEW QUESTION # 54
Which security fabric component sends a notification io quarantine an endpoint after IOC detection "n the automation process?
- A. FortiClient EMS
- B. FortiClient
- C. FortiGate
- D. FortiAnalyzer
Answer: A
Explanation:
* Understanding the Automation Process:
* In the Security Fabric, automation processes can include actions such as quarantining an endpoint after an IOC (Indicator of Compromise) detection.
* Evaluating Responsibilities:
* FortiClient EMS plays a crucial role in endpoint management and can send notifications to quarantine endpoints.
* Conclusion:
* The correct security fabric component that sends a notification to quarantine an endpoint after IOC detection is FortiClient EMS.
References:
FortiClient EMS and automation process documentation from the study guides.
NEW QUESTION # 55
......
Fortinet FCP_FCT_AD-7.4 Exam Practice Test Questions: https://www.examtorrent.com/FCP_FCT_AD-7.4-valid-vce-dumps.html
Free FCP_FCT_AD-7.4 Braindumps Download Updated: https://drive.google.com/open?id=11H6K8cCyiQ9adUOkTcApVyFCVVTq1oix
