

Splunk SPLK-1003 Test Engine Practice Test Questions, Exam Dumps
100% Free SPLK-1003 Daily Practice Exam With 121 Questions
Career Opportunities for Splunk Enterprise Certified Admin
With the Splunk Enterprise Certified Admin certification, individuals have specialized skills and expertise to manage components of Splunk Enterprise environments, such as ensuring a healthy Splunk installation. PayScale states that Splunk System Administrators can earn up to $80k annually.
Generally, the roles available for those certified in Splunk have three main areas: architect, administrator, and developer. Still, there are various career options available for certified specialists in several big data domains, such as Splunk administrators, software engineers, systems engineers, programming analysts, solutions architects, security engineers, technical services manager, and more. Splunk software is used in various fields, from finance and insurance, technical services, retail, manufacturing, to information technology. This creates wide career options for those qualified to use Splunk software.
NEW QUESTION 35
Which feature of Splunk's role configuration can be used to aggregate multiple roles intended for groups of users?
- A. Role inheritance
- B. Linked roles
- C. Role federation
- D. Grantable roles
Answer: A
NEW QUESTION 36
Which feature in Splunk allows Event Breaking, Timestamp extractions, and any advanced configurations found in props.conf to be validated all through the UI?
- A. Forwarder inputs
- B. Apps
- C. Search
- D. Data preview
Answer: C
NEW QUESTION 37
Which setting in indexes. conf allows data retention to be controlled by time?
- A. moveToFrozenAfter
- B. maxDataRetentionTime
- C. frozenTimePeriodlnSecs
- D. maxDaysToKeep
Answer: C
NEW QUESTION 38
Which of the following are supported configuration methods to add inputs on a forwarder? (select all that apply)
- A. Edit forwarder.conf
- B. CLI
- C. Forwarder Management
- D. Edit inputs . conf
Answer: C,D
NEW QUESTION 39
For single line event sourcetypes. it is most efficient to set SHOULD_linemerge to what value?
- A. Newline Character
- B. <regex string>
- C. False
- D. True
Answer: C
NEW QUESTION 40
Which layers are involved in Splunk configuration file layering? (select all that apply)
- A. Global context
- B. App context
- C. Forwarder context
- D. User context
Answer: A,C
NEW QUESTION 41
An index stores its data in buckets. Which default directories does Splunk use to store buckets? (Choose all that apply.)
- A. db
- B. colddb
- C. bucketdb
- D. frozendb
Answer: B,D
NEW QUESTION 42
Which setting in indexes. conf allows data retention to be controlled by time?
- A. frozenTimePeriodlnSecs
- B. moveToFrozenAfter
- C. maxDataRetentionTime
- D. maxDaysToKeep
Answer: B
NEW QUESTION 43
Which forwarder type can parse data prior to forwarding?
- A. Universal forwarder
- B. Heaviest forwarder
- C. Heavy forwarder
- D. Hyper forwarder
Answer: C
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/7.3.1/Forwarding/Typesofforwarders
NEW QUESTION 44
Which Splunk forwarder has a built-in license?
- A. Cloud forwarder
- B. Universal forwarder
- C. Heavy forwarder
- D. Light forwarder
Answer: B
NEW QUESTION 45
Which setting in indexes. conf allows data retention to be controlled by time?
- A. moveToFrozenAfter
- B. maxDataRetentionTime
- C. frozenTimePeriodlnSecs
- D. maxDaysToKeep
Answer: C
Explanation:
https://docs.splunk.com/Documentation/Splunk/latest/Indexer/Setaretirementandarchivingpolicy
NEW QUESTION 46
What are the minimum required settings when creating a network input in Splunk?
- A. Protocol, username, port
- B. Protocol, IP. port number
- C. Protocol, port, location
- D. Protocol, port number
Answer: D
NEW QUESTION 47
How does the Monitoring Console monitor forwarders?
- A. With internal logs forwarded by forwarders.
- B. With internal logs forwarded by deployment server.
- C. By using the forwarder monitoring add-on
- D. By pulling internal logs from forwarders.
Answer: A
NEW QUESTION 48
Which Splunk component performs indexing and responds to search requests from the search head?
- A. Search head cluster
- B. Search peer
- C. License master
- D. Forwarder
Answer: B
Explanation:
Explanation/Reference: https://www.edureka.co/blog/splunk-architecture/
NEW QUESTION 49
Which of the following is accurate regarding the input phase?
- A. Breaks data into events with timestamps.
- B. Fine-tunes metadata.
- C. Applies event-level transformations.
- D. Performs character encoding.
Answer: B
NEW QUESTION 50
In a distributed environment, which Splunk component is used to distribute apps and configurations to the other Splunk instances?
- A. Deployer
- B. Indexer
- C. Deployment server
- D. Forwarder
Answer: C
NEW QUESTION 51
Which of the following must be done to define user permissions when integrating Splunk with LDAP?
- A. Map LDAP to Active Directory
- B. Map LDAP Inheritance
- C. Map Users
- D. Map Groups
Answer: D
NEW QUESTION 52
You update a props.conffile while Splunk is running. You do not restart Splunk and you run this command:
splunk btool props list --debug. What will the output be?
- A. A list of props.confconfigurations as they are on-disk along with a file path from which the configuration is located.
- B. A list of the current running props.confconfigurations along with a file path from which the configuration was made.
- C. A verbose list of all configurations as they were when splunkd started.
- D. A list of all the configurations on-disk that Splunk contains.
Answer: B
Explanation:
Explanation/Reference: https://answers.splunk.com/answers/494219/need-help-with-what-should-be-a-simple- precedence.html
NEW QUESTION 53
Which of the following enables compression for universal forwarders in outputs. conf ?
A)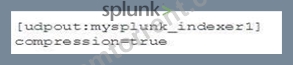
B)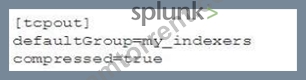
C)
D)
- A. Option D
- B. Option B
- C. Option A
- D. Option C
Answer: A
NEW QUESTION 54
To set up a Network input in Splunk, what needs to be specified'?
- A. Network protocol and port number.
- B. Network protocol and MAC address.
- C. Username and password
- D. File path.
Answer: C
NEW QUESTION 55
The CLI command splunk add forward-server indexer:<receiving-port>will create stanza(s) in which configuration file?
- A. outputs.conf
- B. servers.conf
- C. inputs.conf
- D. indexes.conf
Answer: C
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Forwarder/8.0.5/Forwarder/Enableareceiver
NEW QUESTION 56
When running the command shown below, what is the default path in which deployment server. conf is created?
splunk set deploy-poll deployServer:port
- A. SPLUNK_HOME/etc/system/local
- B. SPLUNK_HOME/etc/system/default
- C. SPLUNK_KOME/etc/apps/deployment
- D. SFLUNK_HOME/etc/deployment
Answer: A
NEW QUESTION 57
......
Use Valid New SPLK-1003 Test Notes & SPLK-1003 Valid Exam Guide: https://www.examtorrent.com/SPLK-1003-valid-vce-dumps.html
SPLK-1003 exam torrent Splunk study guide: https://drive.google.com/open?id=1NWVMst_w1TLyHrai8pmOxkPVOEw448UC
